Security and compliance
Your data, protected at every layer.
Student and staff records are sensitive. Here is exactly how Scholva protects them, in plain language, not legal boilerplate.
How it works
Five layers, working together.
From the database to the settings screen, security is not a separate feature. It is how the product is built.
Encrypted everywhere
Data at rest is encrypted with AES-256. Every connection, browser session and API call runs over TLS 1.2 or higher.
Backed up daily
Daily encrypted backups with a 30-day retention period, so a bad afternoon never costs you a term's worth of records.
Secure hosting
Scholva runs on cloud infrastructure with restricted, multi-factor-authenticated access, and is governed by the laws of India.
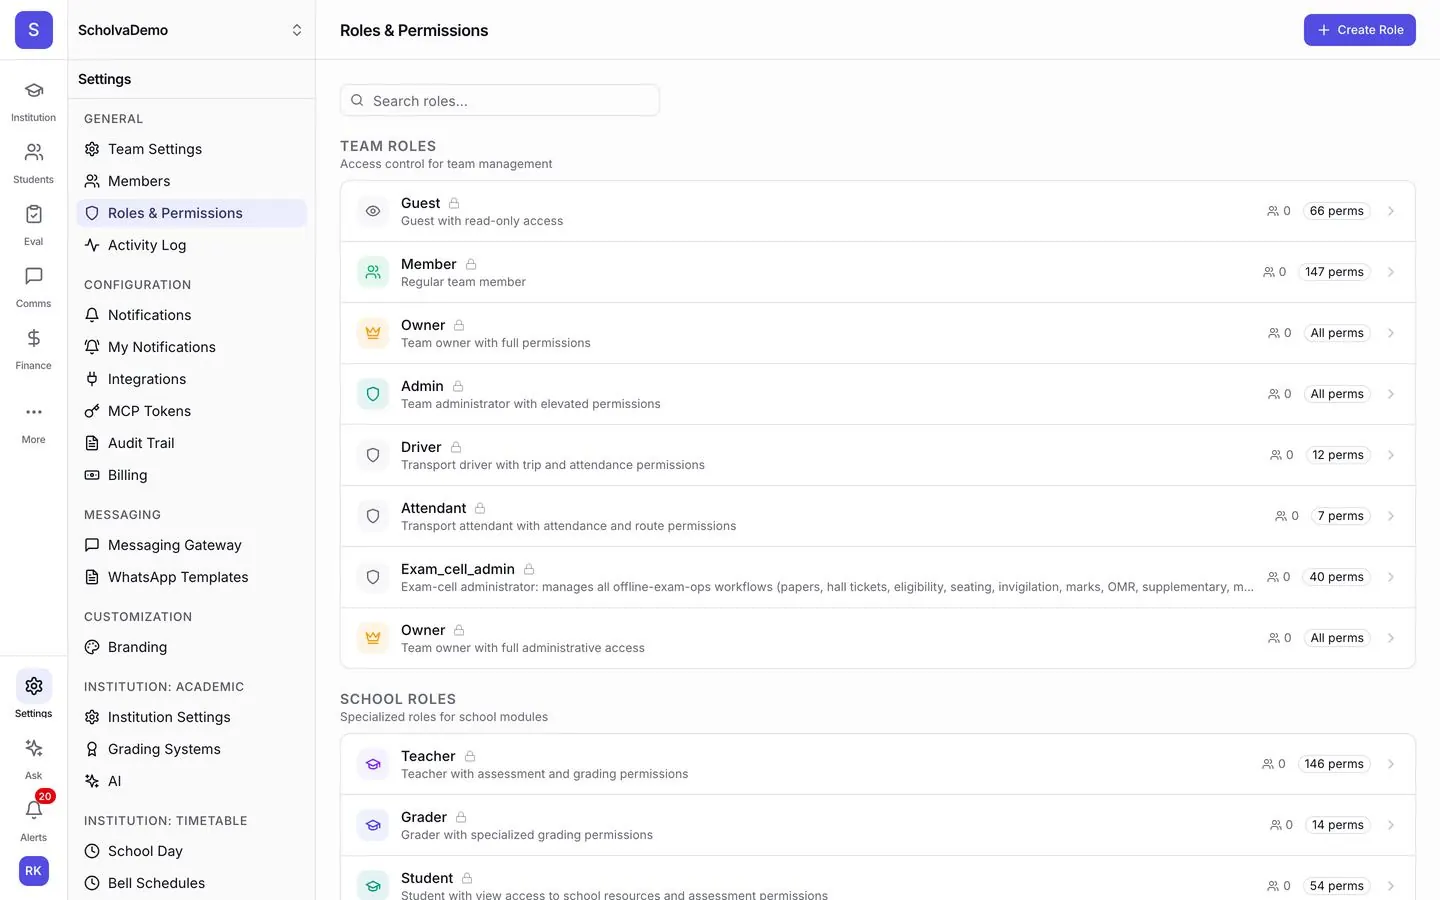
Roles and audit trails
Every team and school role, from owner to exam cell admin, gets exactly the permissions it needs and nothing more, with a log of who changed what.
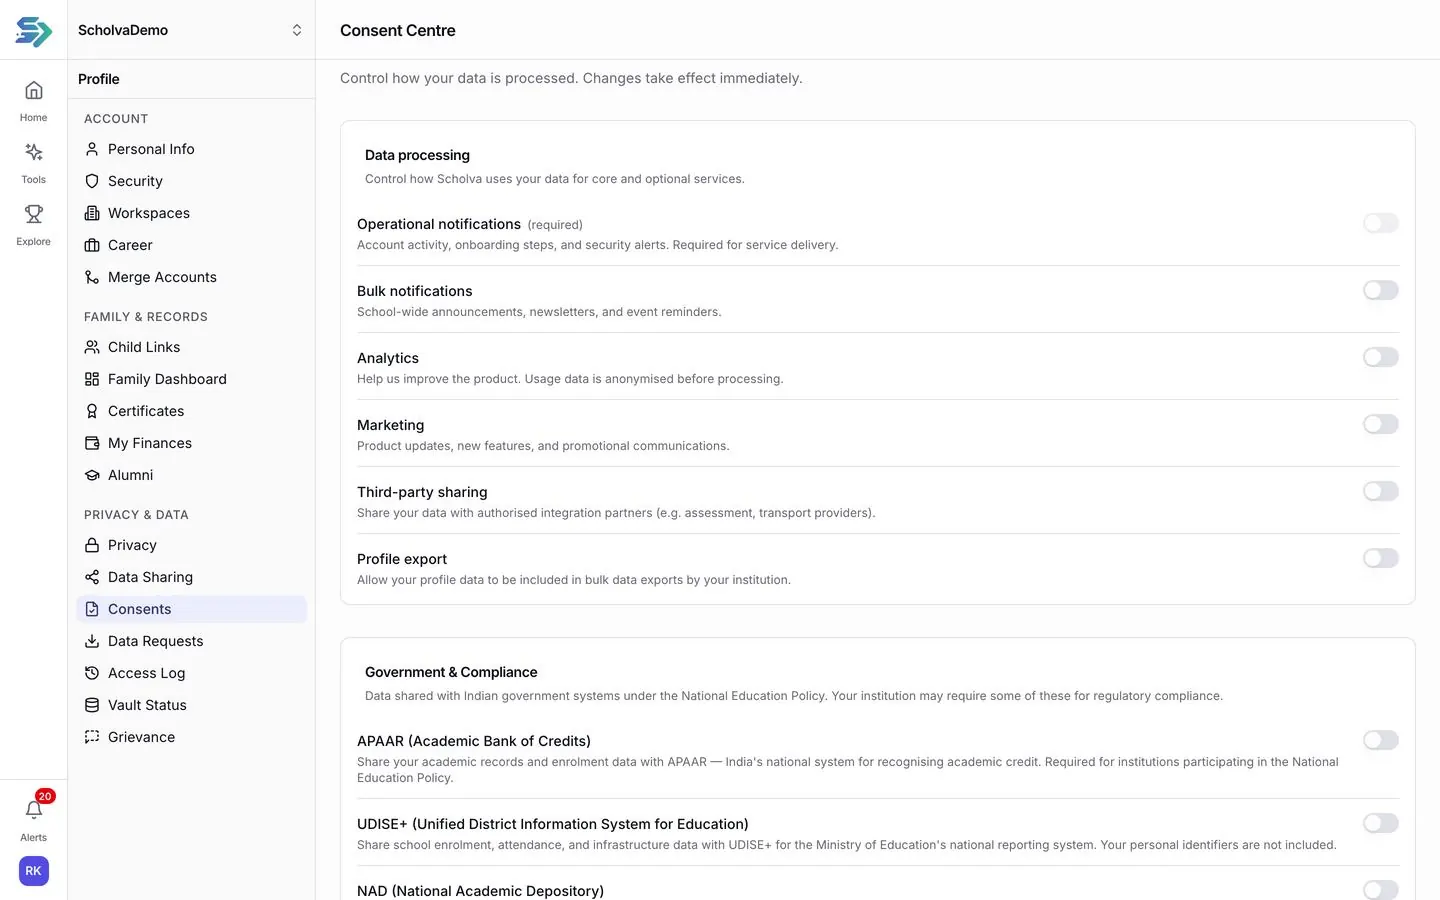
DPDP consent, built in
A consent centre for data processing, notifications, analytics and third-party sharing, plus APAAR and UDISE+ consents, for every family.
Compliance
Built for how Indian schools are regulated.
We take the DPDP Act and our obligations as a data processor seriously, in writing, not just in a badge on this page.
Designed around the DPDP Act
Consent management, data export and erasure requests, and an access log, aligned with India's Digital Personal Data Protection Act, 2023.
A Data Processing Agreement for every school
We act as a data processor. A DPA setting out our obligations is available for every institution that asks for one.
Documented incident response
A written incident response plan, regular drills, and notification of the data controller without undue delay, within 72 hours where feasible.
Data portability, no lock-in
Request your data in a structured, machine-readable format at any time. Nothing is held hostage in a proprietary export.
The numbers behind the promise.
99.9%
Uptime
AES-256
Encryption at rest
72hr
Breach notification window
30 day
Backup retention
Questions
Security, answered plainly.
Still have a question for your board or your IT lead? Our team is happy to walk through it.